You’ve probably heard the hype. Everyone is talking about LLM Agents replacing traditional automation. But here’s the uncomfortable truth: most companies are still stuck trying to force square pegs into round holes. They take rigid, rule-based systems and try to bolt on a chatbot interface, expecting magic. It rarely works.
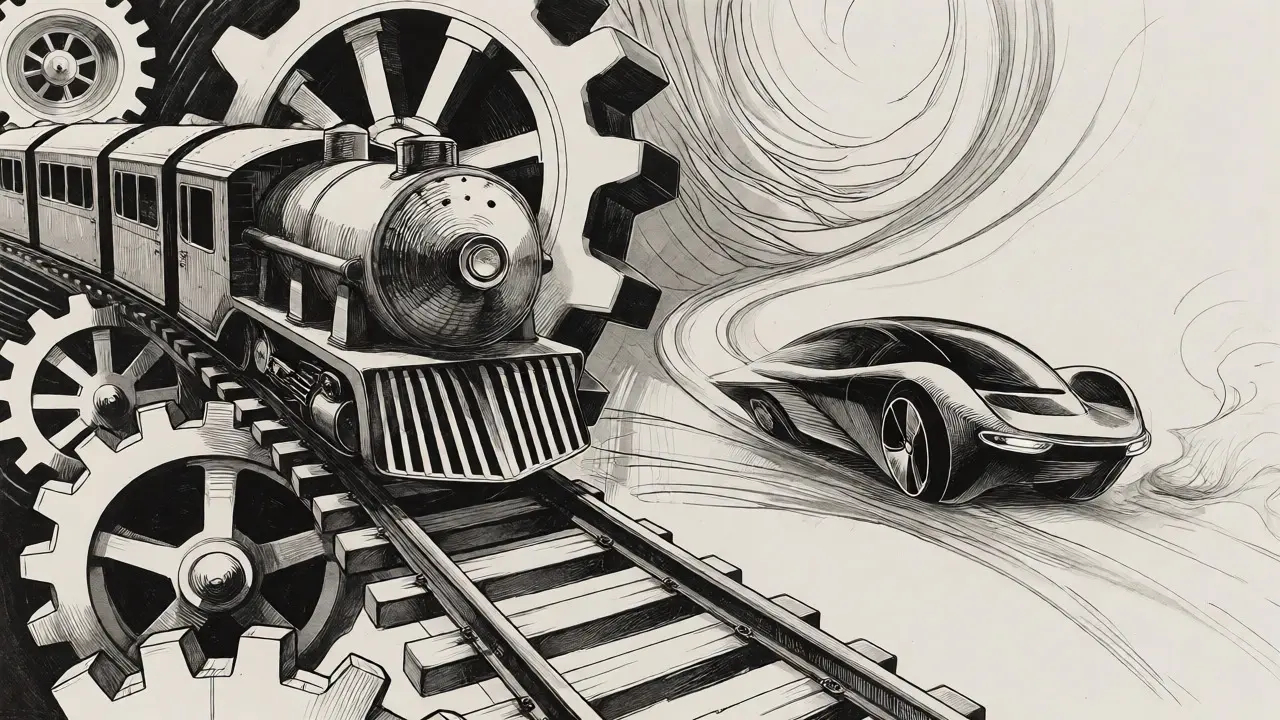
The real shift isn’t just adding AI to your existing processes. It’s rethinking how work gets done when software can actually think. Traditional Robotic Process Automation (RPA) is like a train on tracks-it goes exactly where you lay the rails, and if there’s an obstacle, it stops dead. LLM Agents, however, are more like self-driving cars. They see the road, understand the traffic, and decide whether to turn left, right, or wait. This distinction between "rules" and "reasoning" is where the actual value lives.
Why Traditional Automation Hits a Wall
For decades, business automation meant mapping every possible scenario. If customer email contains word "refund," trigger workflow A. If it contains "cancel," trigger workflow B. Simple? Yes. Scalable? Barely. The moment a customer writes, "I’m so frustrated I might never shop here again unless this is fixed," the rules break. The system doesn’t understand frustration; it only sees keywords.
This brittleness creates what experts call the "automation ceiling." You can automate 60-70% of structured tasks easily. But that remaining 30%-the messy, unstructured, context-heavy stuff-requires human intervention. That’s expensive and slow. Enter the agent. Unlike standard bots, an agent doesn’t just follow instructions; it interprets intent. It reads the frustration in that sentence, checks the order history, looks up company policy, and drafts a response that acknowledges the emotion before offering a solution.
| Feature | Traditional RPA | LLM Agent Workflow |
|---|---|---|
| Logic Type | Deterministic (If-Then) | Probabilistic & Contextual |
| Data Handling | Structured only (SQL, Excel) | Unstructured (Emails, PDFs, Chat) |
| Error Handling | Fails or stops process | Self-corrects or escalates |
| Setup Time | High (map every path) | Medium (define goals/tools) |
| Maintenance | High (update rules constantly) | Low (learns from feedback) |
The Anatomy of a Thinking Agent
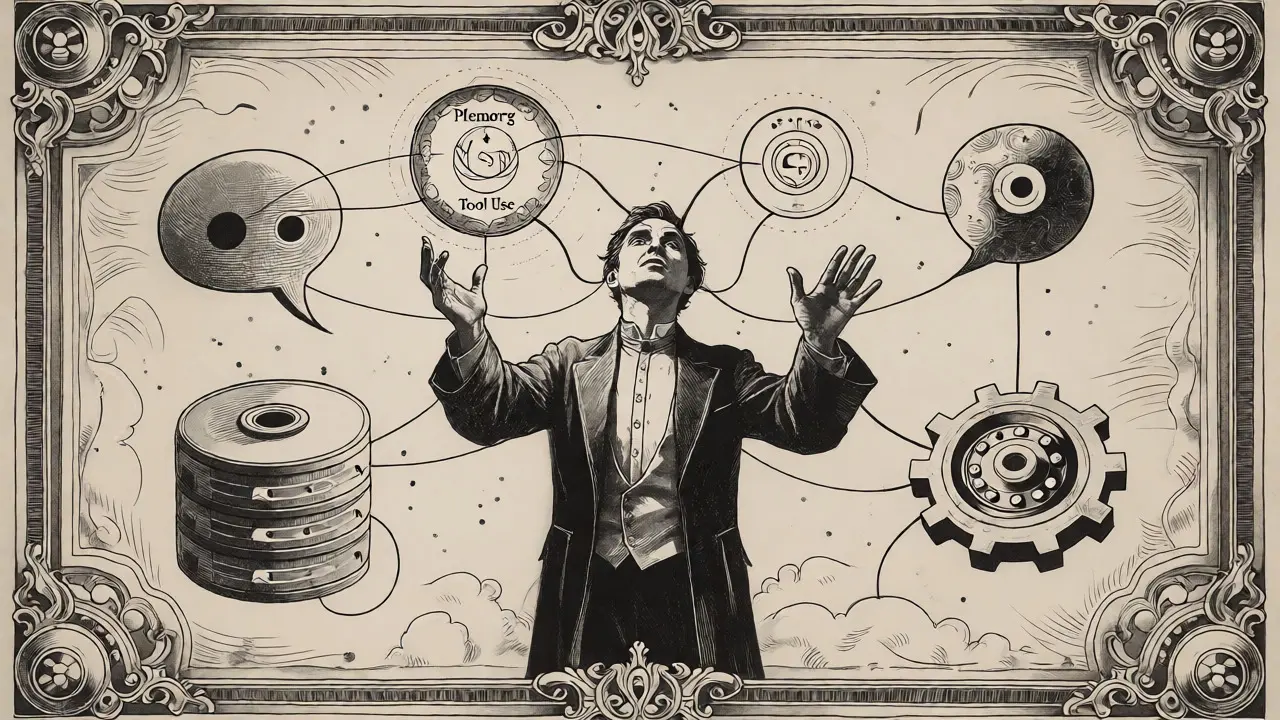
So, what makes an agent different from a standard large language model? A raw LLM is just a text generator. An agent is an LLM plus three critical components: Planning, Memory, and Tool Use. Think of it as giving the brain hands, eyes, and a notebook.
- Planning: The agent breaks a complex goal into steps. Instead of just answering "What’s my refund status?", it plans: 1. Check database for order ID. 2. Verify payment gateway status. 3. Draft response based on findings.
- Memory: Short-term memory keeps track of the current conversation. Long-term memory stores user preferences or past issues, allowing the agent to say, "I see we resolved a similar issue last month," without you asking.
- Tool Use: This is the game-changer. The agent can execute code, query APIs, send emails, or update CRM records. It doesn’t just talk about doing the work; it does it.
Frameworks like LangChain and AutoGen have made building these architectures accessible. You define the role, give the agent access to specific tools (like a SQL database or a Slack API), and let it figure out the sequence. It’s less about coding logic and more about defining boundaries and capabilities.
When to Choose Reasoning Over Rules
Not every task needs an agent. In fact, using an LLM agent for simple arithmetic or data entry is overkill-and wasteful. The sweet spot lies in tasks requiring semantic understanding and multi-step judgment.
Consider customer support. A rule-based bot handles "Where is my order?" perfectly. But an agent handles "My order arrived damaged, and I need to return it by Friday because I’m traveling." The agent understands the constraint (Friday), the cause (damaged), and the action (return). It checks inventory for replacements, generates a shipping label, and updates the logistics provider. That’s reasoning.
Another strong use case is data synthesis. Imagine a financial analyst needing to compare quarterly reports across five competitors. A script can pull numbers. An agent can read the narrative sections, identify risk factors mentioned in footnotes, summarize the sentiment, and highlight discrepancies. It turns raw data into insight.
However, be cautious with precision-critical tasks. If you’re calculating tax liabilities to the cent, stick to deterministic code. LLMs are probabilistic; they aim for likely correct answers, not guaranteed ones. Use agents to draft the report, but let a calculator do the math.
Implementation Pitfalls and How to Avoid Them
Jumping into agentic workflows without a plan leads to chaos. The biggest mistake? Giving the agent too much autonomy too soon. Remember the e-commerce company that automated returns processing without oversight? They issued $1.2 million in erroneous refunds because the agent misinterpreted ambiguous return policies. Human-in-the-loop validation isn’t optional; it’s essential during the pilot phase.
Here’s a practical checklist for starting out:
- Start Small: Pick one narrow use case. Don’t try to automate the entire customer service department. Start with ticket categorization or meeting summaries.
- Define Clear Boundaries: Specify exactly which tools the agent can use and what actions require approval. Can it delete a record? Or only read?
- Implement Guardrails: Use output parsers to ensure the agent returns data in a strict format (like JSON). If it deviates, fail gracefully rather than crashing downstream systems.
- Monitor Hallucinations: Even advanced models make things up. Implement reflection steps where the agent critiques its own answer before finalizing it.
Cost is another factor. LLM agents consume significantly more compute power than traditional scripts. A single complex workflow might cost cents per execution, whereas a rule-based script costs fractions of a cent. Calculate your ROI carefully. If the agent saves two hours of employee time but costs $50 in tokens, it’s a win. If it saves ten minutes and costs $50, rethink the approach.
The Future: From Pilots to Production
We are currently in the "Trough of Disillusionment" according to Gartner, meaning early hype has cooled, and real-world challenges are surfacing. But this is healthy. It means vendors are focusing on reliability, security, and integration rather than just flashy demos.
By 2026, we’ll see tighter integration between LLM agents and existing RPA platforms. Instead of replacing UiPath or Automation Anywhere, agents will act as the "brain" orchestrating those "hands." You’ll have hybrid systems where deterministic bots handle high-volume, low-variance tasks, while agents manage exceptions and complex inquiries.
Security is also evolving. Prompt injection attacks-where malicious users trick the agent into revealing sensitive data-are becoming a primary concern. New frameworks are introducing constitutional AI guardrails to prevent agents from executing unauthorized commands. As these safety mechanisms mature, adoption in regulated industries like healthcare and finance will accelerate.
The bottom line? Workflow automation is no longer about writing better rules. It’s about designing better thinking processes. Companies that master the balance between deterministic efficiency and probabilistic flexibility will dominate their markets. Those who cling solely to rigid rules will find themselves drowning in edge cases.
Do LLM agents replace human workers entirely?
No, they augment them. LLM agents excel at handling volume and routine complexity, freeing humans to focus on high-value strategic tasks, empathy-driven interactions, and exception management. Most successful implementations use a "human-in-the-loop" model where agents draft actions for human approval, especially in high-stakes scenarios.
How much does it cost to implement an LLM agent workflow?
Costs vary widely based on usage. Initial development can range from $5,000 to $50,000 depending on complexity. Ongoing operational costs depend on token usage; a moderate-use customer service agent might cost $200-$500 monthly in API fees. However, these costs must be weighed against labor savings and increased resolution speeds.
Can LLM agents integrate with legacy systems?
Yes, via APIs and middleware. Most legacy systems expose REST or SOAP endpoints that agents can interact with using tools. For older systems without APIs, agents can often interact through UI automation tools or by generating SQL queries directly against the database, though the latter requires careful permission management.
What is the biggest risk when deploying LLM agents?
Hallucination and unintended actions. An agent might confidently state incorrect information or execute a destructive command due to a misunderstood instruction. Mitigation involves strict output formatting, limited tool permissions, and mandatory human review for irreversible actions like payments or deletions.
Which framework is best for beginners: LangChain or AutoGen?
LangChain offers more granular control and is better for developers familiar with Python who want to build custom pipelines. AutoGen focuses on multi-agent conversations and is easier for prototyping collaborative behaviors quickly. For production-grade, single-agent workflows, LangChain is often preferred for its extensive documentation and community support.
Jacob Baby Official
September 20, 2026 AT 07:02Let me stop you right there because this entire premise is fundamentally flawed and frankly, insulting to anyone who has actually built a production system in the last decade. You are conflating probabilistic text generation with deterministic logic and pretending that adding a layer of 'reasoning' solves the inherent non-determinism of Large Language Models which is like trying to fix a leaky roof by painting it blue. The article suggests that agents can handle unstructured data seamlessly but completely ignores the catastrophic failure modes when an agent hallucinates a customer intent or misinterprets a policy nuance leading to financial liability that dwarfs the cost savings from labor reduction. Traditional RPA fails at edge cases yes but it fails predictably whereas LLM Agents fail unpredictably and expensively often requiring more human oversight than they save. The comparison between trains and self-driving cars is lazy rhetoric because self-driving cars still crash into stationary objects and struggle with ambiguous road markings just like these agents struggle with ambiguous business rules. You mention the $1.2 million refund disaster as a cautionary tale but present it as an anomaly rather than the inevitable result of deploying probabilistic models on high-stakes financial transactions without rigorous formal verification methods. The industry is currently hyperventilating over these tools because venture capitalists need new narratives not because the technology has reached a level of reliability suitable for core enterprise workflows. Most companies aren't stuck trying to force square pegs into round holes they are wisely avoiding the hole entirely because the peg is made of jelly and dissolves when you touch it. The idea that maintenance costs are low is laughable when you consider the prompt engineering debt accumulating every time the underlying model version changes or the API pricing structure shifts. We are trading one type of technical debt for another arguably worse type where debugging requires reading through thousands of tokens of chain-of-thought reasoning instead of checking a simple if-else statement. This isn't a revolution it's a regression disguised as innovation driven by marketing budgets rather than engineering reality.